
Some Notion AI chats were exposed through one of Notion's AI vendors
A security incident at Fireworks AI, one of Notion's AI vendors, exposed some Notion AI chat transcripts. Notion says under 1% of workspaces are affected.
By Agentico team ·
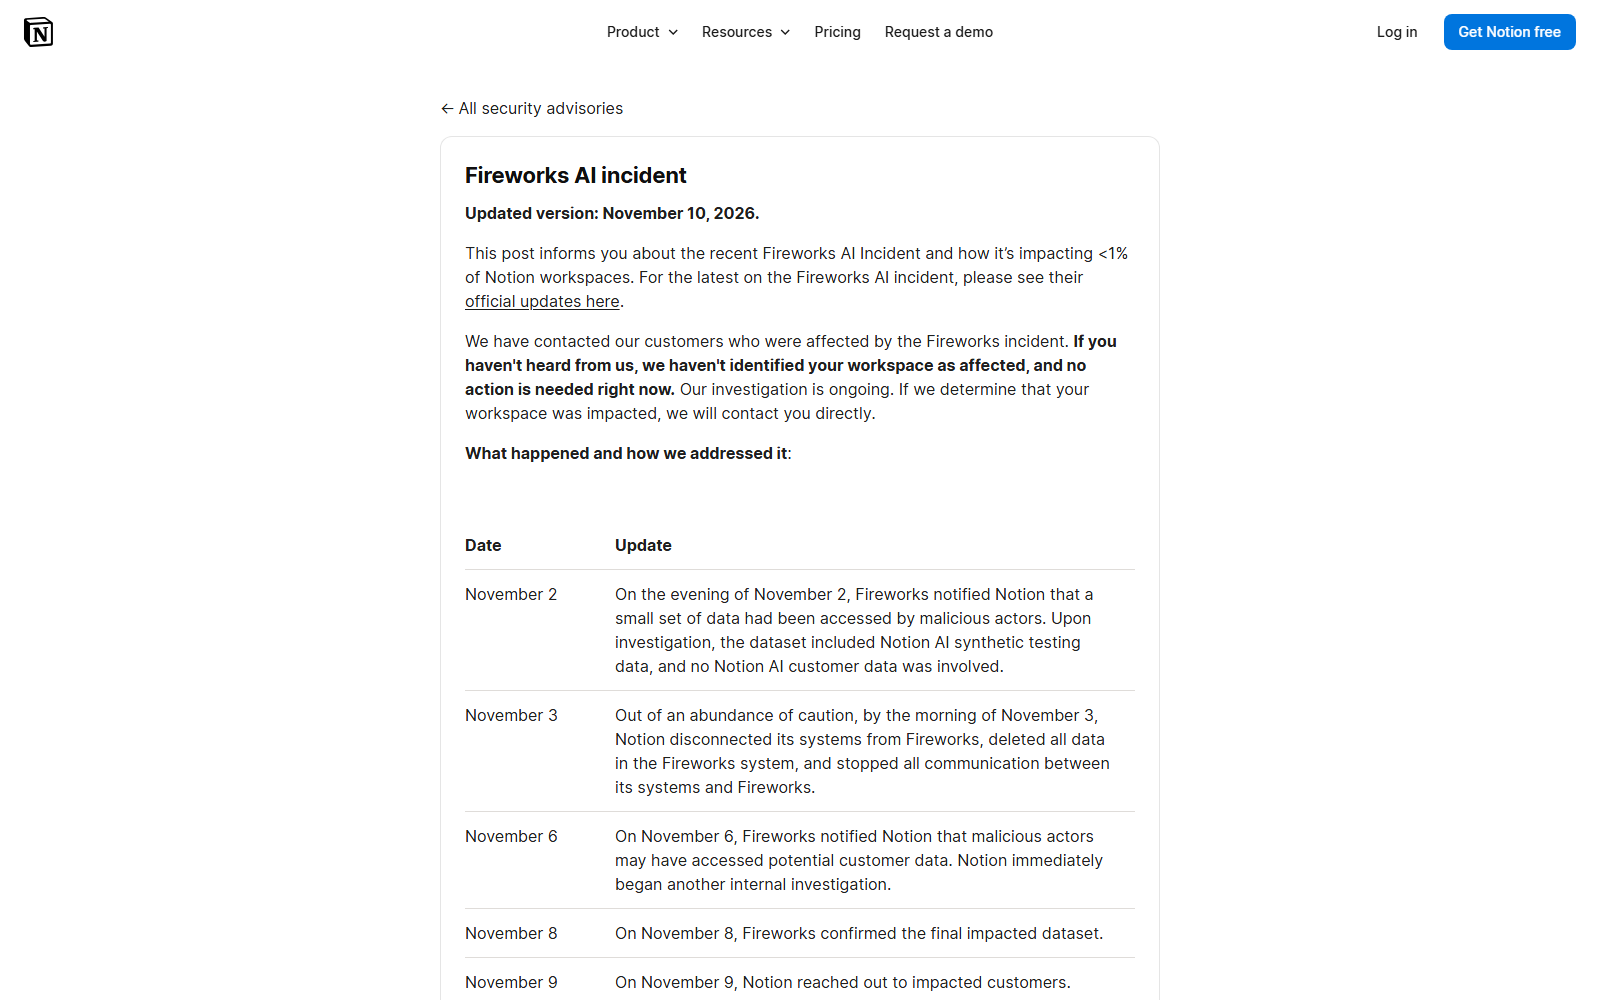
Notion says some chat transcripts from its AI assistant were exposed in a security incident at Fireworks AI, one of the AI companies it used. In a security advisory updated on 10 November, Notion says fewer than 1% of workspaces are affected and that this wasn't a breach of its own systems.
Notion's timeline says Fireworks first told it on 2 November that a small set of data had been accessed, which turned out to be Notion AI test data, not customer data. By the morning of 3 November, Notion had disconnected its systems from Fireworks and deleted its data there. On 6 November, Fireworks said customer data may also have been accessed, and on 8 November it confirmed the final dataset. Notion contacted affected customers on 9 November.
What was exposed
The dataset included Notion AI chat transcripts used for Insights, a feature that shows workspace admins how their team uses AI. Notion says that for the vast majority of affected workspaces the transcripts were "unattributable", meaning they weren't labelled with who wrote them or which workspace they came from. They didn't contain tool call results, and Notion says no other features were affected.
Its help centre says a transcript includes anything that went into or came out of the model in the chat. The Register reports that, as Reddit users pointed out, the conversations themselves could still contain identifying details.
Notion's help centre also says Fireworks had given it a contractual commitment not to retain its data, but Notion's investigation found data had been kept from the Fireworks endpoints it used. Notion has turned off Insights, stopped using Fireworks to run open-weight models and is auditing its critical vendors, such as inference providers and data processors.
What happened at Fireworks
Fireworks' own update says a cloud provider that hosted its research and development machines had a security incident on 23 October. The next day, the attacker used it to reach Fireworks development machines and run an unauthorised workload that affected more customer data. Fireworks says the evidence points to a financially motivated group that sells unauthorised access to AI models, and it's working with Palo Alto Networks' Unit 42. The Register reports this is the second incident Fireworks has disclosed in October. Neither Notion nor Fireworks says which incident the Notion data came from.
What to do
If you use Notion, ask whoever owns your workspace whether Notion has been in touch. Notion says that if neither you nor your workspace owner has heard from it, it hasn't identified your workspace as affected and no action is needed right now, though its investigation is ongoing. Owners of affected workspaces can review the data in a desktop browser by opening the ? menu in the sidebar and choosing Security incident review, Notion's help centre says.
Notion recommends that affected customers treat the data as exposed, and rotate any passwords, API keys or other credentials pasted into Notion AI during the timeframe of the incident.
Whatever tools you use, it's a good habit to keep passwords and keys out of AI chats. This incident happened at a company Notion used in the background, so it's also worth checking which AI companies your main business tools send data to, on their security or trust pages, and removing connected apps you no longer need.
Sources
- Fireworks AI incident (security advisory), Notion
- Notice about the Fireworks AI incident that may impact some Notion workspaces, Notion Help Center
- Update on October 2026 security incident, Fireworks AI
- Fireworks AI gets burned twice as customer data exposure widens, The Register
We help Sunshine Coast businesses put AI to work on the systems they already use. If you'd like to talk through what this means for yours, book a free call.
Book a free call